tl;dr
- By default, new Amazon S3 buckets are private. To share files publicly, you need to make them accessible to others.
- Making an S3 Bucket Public:
- Go to S3 Management Console > Permissions tab > Block Public Access.
- Uncheck “Block all public access” and save.
- To make the entire bucket and its contents public, go to Permissions > Bucket policy > Edit and paste in the appropriate policy (see below).
- Finding the S3 Bucket URL & Individual Object URL:
- Open the bucket and stay on the Objects tab.
- Click the file name, then copy the Object URL from the object’s details page.
- Finding the S3 Bucket Endpoint:
- Click on the bucket name > Properties tab > Static Website Hosting card.
- The website endpoint is listed there, once static website hosting is turned on.
- NB: Amazon discourages granting public access to an S3 bucket due to security concerns.
If you’re using an Amazon S3 bucket to share files with anyone else — such as sharing images publicly from a shoot with clients — you’ll first need to make those files public. By default, new buckets are set to be private. Making the contents public will make them accessible to others.
Maybe you’re sending download links to someone, or perhaps you’re using S3 for static files for your website or as a content delivery network (CDN). I often use it to share images with clients or just make them publicly accessible in a quick and simple way. There are certainly more specialized ways to do this, but sometimes what I want is just the quick and simple route, even if it doesn’t come with fancy features.
But a common problem you might run into is that if you don’t explicitly make the files public, your users will get an XML Access Denied error message saying the file is unavailable.
That page is served with an HTTP 403 response, so depending on what’s fetching the file you might see it reported as 403 Forbidden instead of as the Access Denied XML page. It’s the same problem either way, and the fix below is the same.
It’s relatively straightforward to make S3 buckets public, but it’s not necessarily self-evident how to do it. It has also changed from an older method that no longer works since Amazon revamped its permissions processes. (This post used to show the older method, but I’ve now updated it below with the new method.)
I’m focusing here on making an entire bucket and all of its contents public. So before you make the changes, please be sure that you don’t have any files in there that you don’t want accessible to everyone on the internet. It is quite possible to make individual files (or objects) public on a file-by-file basis; I’ll cover that further down this page.
But for situations where you don’t want to be messing with permissions for each individual file — say, if you’re using an S3 bucket to share photos from a whole shoot with clients or as the storage source for your website’s CDN — you can also make the entire bucket publicly accessible. That includes all of its existing contents and any new files uploaded to it.
So a big advantage of doing it this way is that it will apply to all files you add to the bucket in the future as well. This means you should only have to do this once per bucket. But it also means that you definitely don’t want to do this if you’re using the bucket as a cloud backup of your computer.
There are also multiple ways to handle the issue. While this is among the quickest and simplest, it’s not the only method and not even necessarily the best for all uses. Access control lists (ACLs) used to be the more precise way to do it, file by file, but Amazon now disables ACLs on every new bucket by default — the Object Ownership setting is set to “bucket owner enforced” — and recommends bucket policies instead. If you want to use ACLs on a new bucket, you have to switch Object Ownership back on in the bucket’s Permissions tab first.

Making a new S3 bucket public while you create it
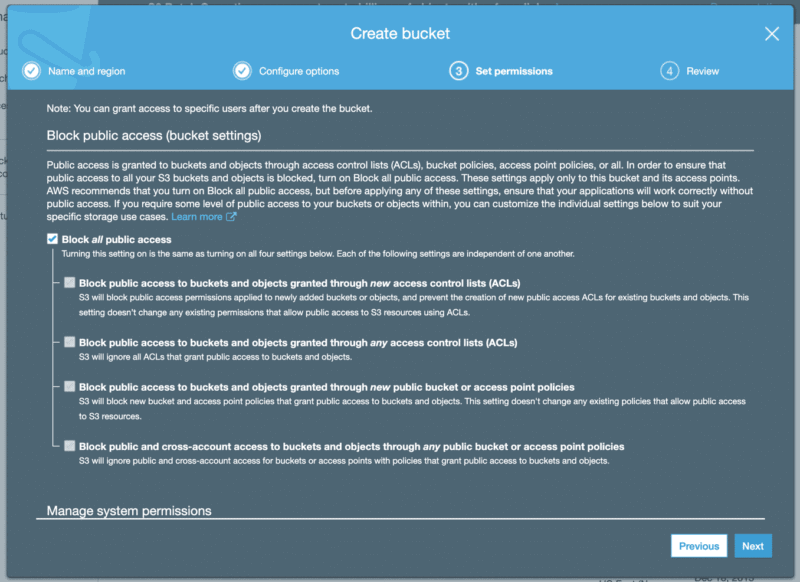
When you create a new bucket, there’s a new step-by-step process that is much more user-friendly than the old version.
Step 3 in that process is to set permissions. By default, new buckets are set to Block all public access. In other words, no one else can access the files.
You can uncheck that option, but on its own it doesn’t make anything public. All it does is lift the block, so that a bucket policy can then grant read access. You still need to add the policy further down this page before anyone can view or download the files.
How to make an S3 bucket public
Here’s how to do it for one S3 bucket at a time.
1. Sign in to Amazon Web Services and go to your S3 Management Console.
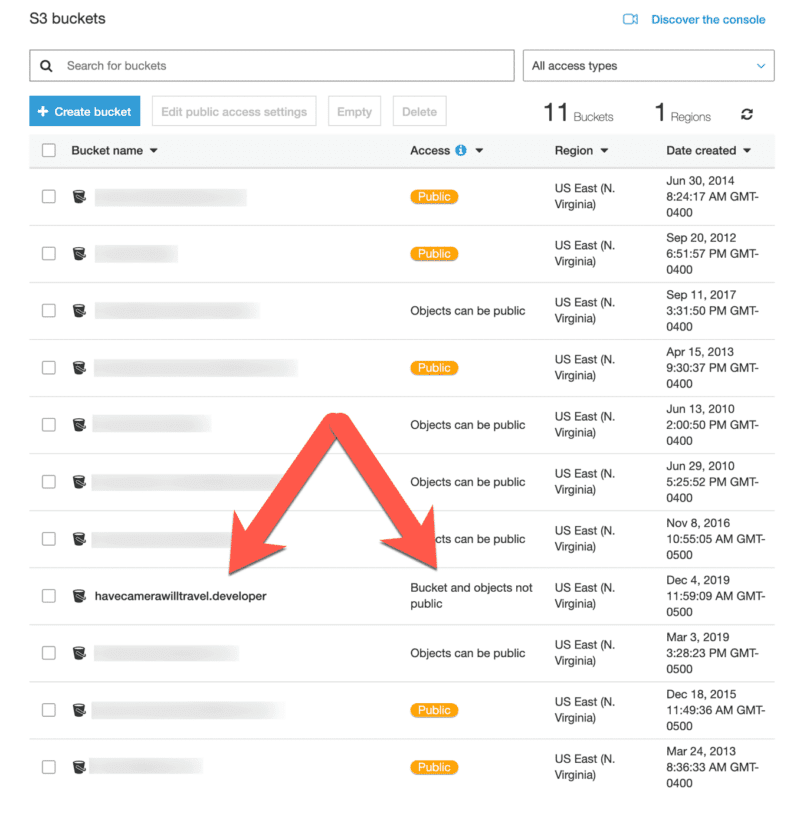
2. Click on the name of the S3 bucket from the list. If it’s still in its default access state, it should say “Buckets and objects not public” next to it.
3. Go to the Permissions tab. The first section on that page is Block public access (bucket settings), and “Block all public access” will be On. Click the Edit button at the right.
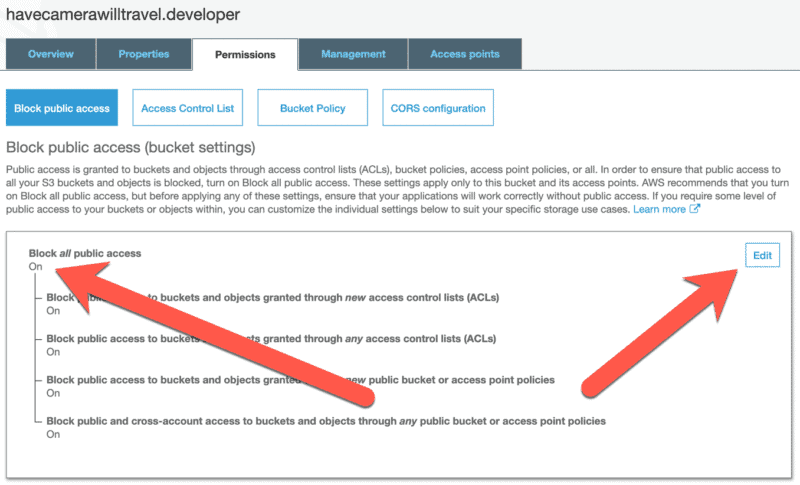
4. Uncheck the “Block all public access” option, and then click the Save button.
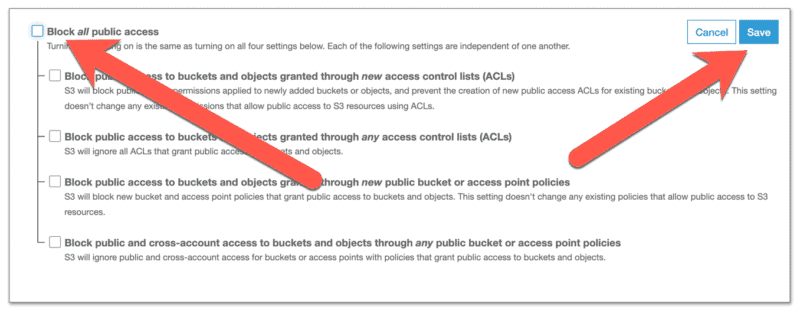
You’ll then be asked to confirm the change by typing in the word confirm.
Making everything in the S3 bucket publicly accessible
If you go back to the S3 buckets list, you’ll see that the access for that bucket has now been changed to “Objects can be public.” And that’s where the official Amazon instructions stop.
But I’m guessing that the reason you’re here is that you’ve discovered that doesn’t actually make the entire bucket public. If you try to access (read) the files now through a web browser, for instance, you’ll still get the Access Denied error.

So we can take it a step further and make an entire bucket, all of its existing contents, and any new files uploaded to it, publicly accessible.
But before proceeding, know that Amazon discourages granting public access to an S3 bucket and will show you a warning to that effect when you save the Bucket Policy below. If you proceed, this is going to make all the bucket’s contents available to anyone with an internet connection to read, view, and download.
1. From the bucket list, click on the bucket name again. Select the Permissions tab again, then scroll down to the Bucket policy section and click Edit. That opens the Edit bucket policy page.
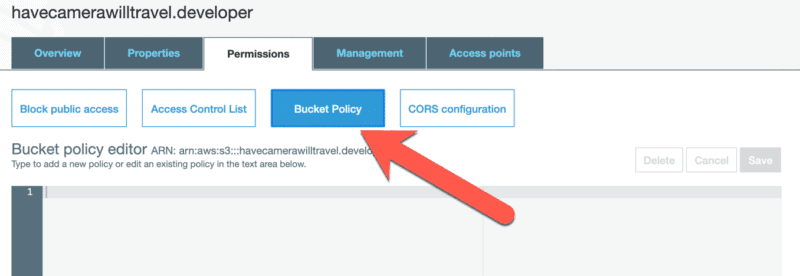
2. Copy and paste this code into the Policy entry area. You’ll need to replace “YOUR-BUCKET-NAME” with your full bucket name.
{"Version": "2008-10-17",
"Statement": [{"Sid": "AllowPublicRead",
"Effect": "Allow",
"Principal": {
"AWS": "*"
},
"Action": "s3:GetObject",
"Resource": "arn:aws:s3:::YOUR-BUCKET-NAME/*"
}]}
As an example, if your bucket is named “havecamerawilltravel.developer”, as in the example I’m using here, it should look like the screengrab below.

When you click Save, you’ll get a warning:
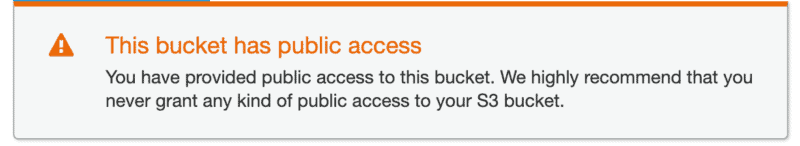
If you want to heed that warning and remove the public access, you can use the Delete button above the input area.
Now, when you go back to the bucket list, you’ll see that the entry in the access column has changed to public.

How to find the S3 bucket URL & the URL for an individual object
There are a number of ways to share the contents of the bucket, from an individual URL for an individual object through making the bucket available to host a static website on a custom domain.
If you’re looking to quickly share the URL of a specific S3 object, here’s one way to find the link:
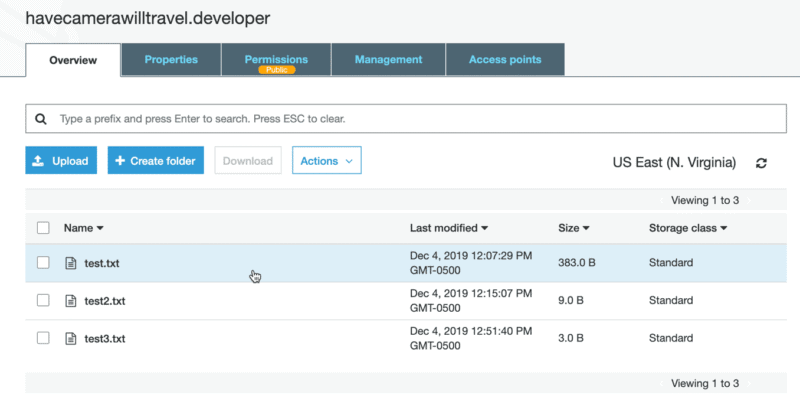
1. From the bucket list, click on the name of the bucket. The list of files in the bucket is on the Objects tab, which opens by default.
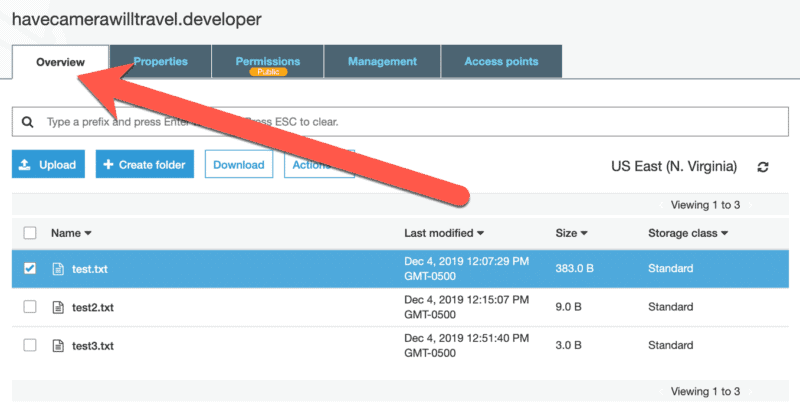
2. Use the search bar to locate the file, if necessary. Then click on the file name to open the object’s details page.
3. In the Object overview section at the top of that page, you’ll find the Object URL field. That’s the file’s public link.
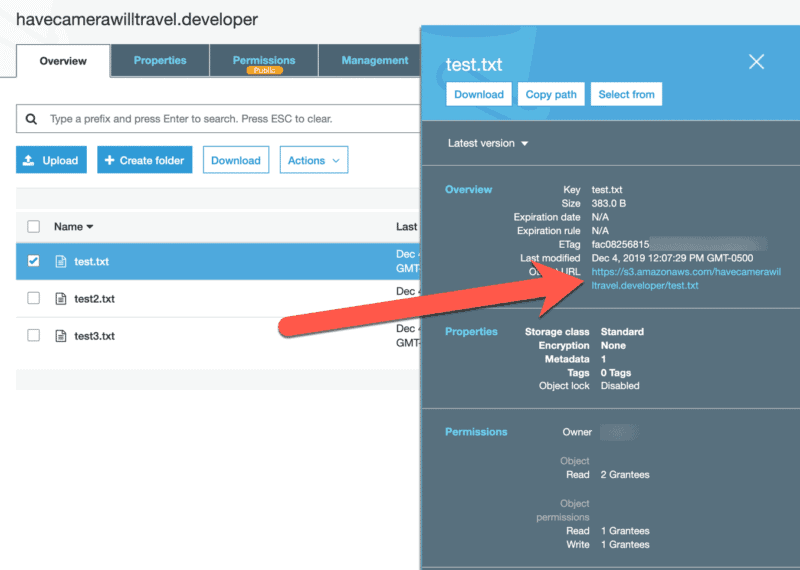
You can then send that link to others to download or open.
There’s also a Copy S3 URI button nearby, and it’s easy to grab the wrong one. The S3 URI starts with s3:// and is meant for the AWS command line and SDKs — paste it into a browser and nothing will happen. It’s the Object URL, starting with https://, that you send to other people.
How to find an Amazon S3 bucket endpoint
Some applications, such as plugins for website platforms or backups apps, might ask for your bucket’s endpoint. That’s the location displayed in a standard URL format (as opposed to a local path, for instance). It’s also sometimes called the S3 URL.
Two different addresses get called the endpoint, though, and they’re not interchangeable. The one in the Static website hosting section is the website endpoint, and it looks like http://your-bucket.s3-website-us-east-1.amazonaws.com. It only exists once you’ve enabled website hosting, and it’s HTTP only — there’s no HTTPS version of it. The address most plugins and backup apps actually want is the REST endpoint, which works whether or not website hosting is on: https://your-bucket.s3.us-east-1.amazonaws.com, or https://s3.us-east-1.amazonaws.com with the bucket name as the first part of the path.
Here’s a quick way to find the endpoint URL.
1. Click on the bucket name from the list of S3 buckets.
2. Go to the Properties tab.
3. Scroll to the bottom of the Properties tab to the Static website hosting section. The bucket website endpoint is listed there — but only once static website hosting has been turned on. If it’s still disabled, there’s no website endpoint to copy yet.
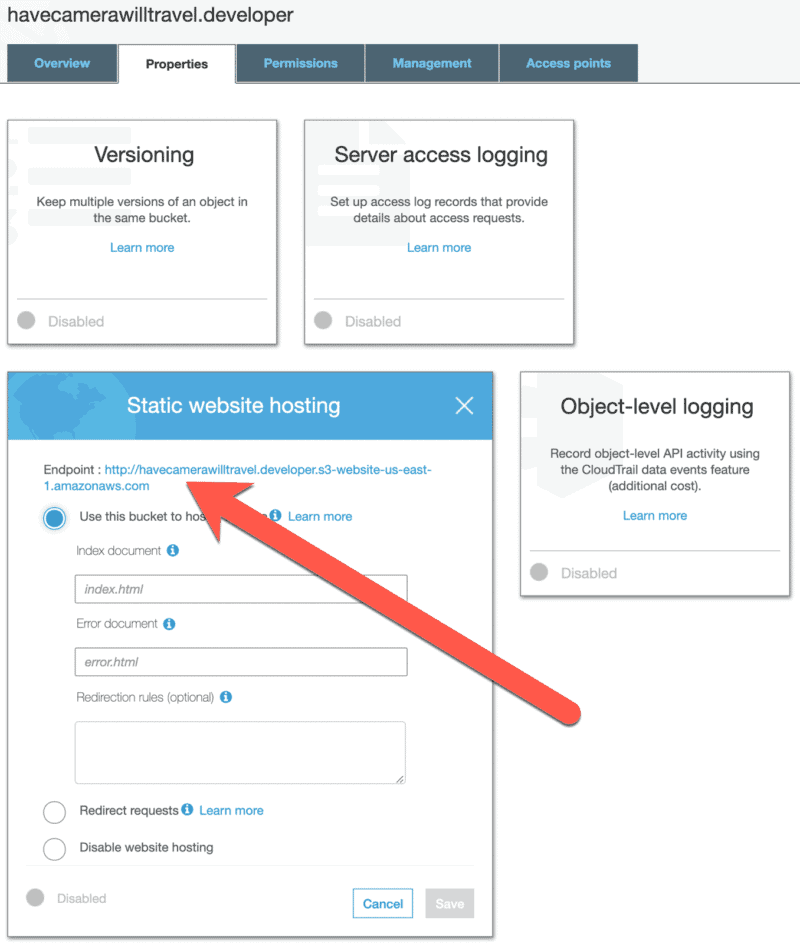
If you’re going to set up the bucket to host a static website, there’s more to it. You can find Amazon’s instructions on the rest of that process here.